Ransomware Leak-Site Tracker: See Who's Being Named, and Check Your Own Domain
Modern ransomware is double extortion: steal data, then name the victim on a dark-web leak site with a countdown to publication. Our new free tracker maps these claims worldwide — and every 2MNY scan now checks your domain against the dataset automatically.
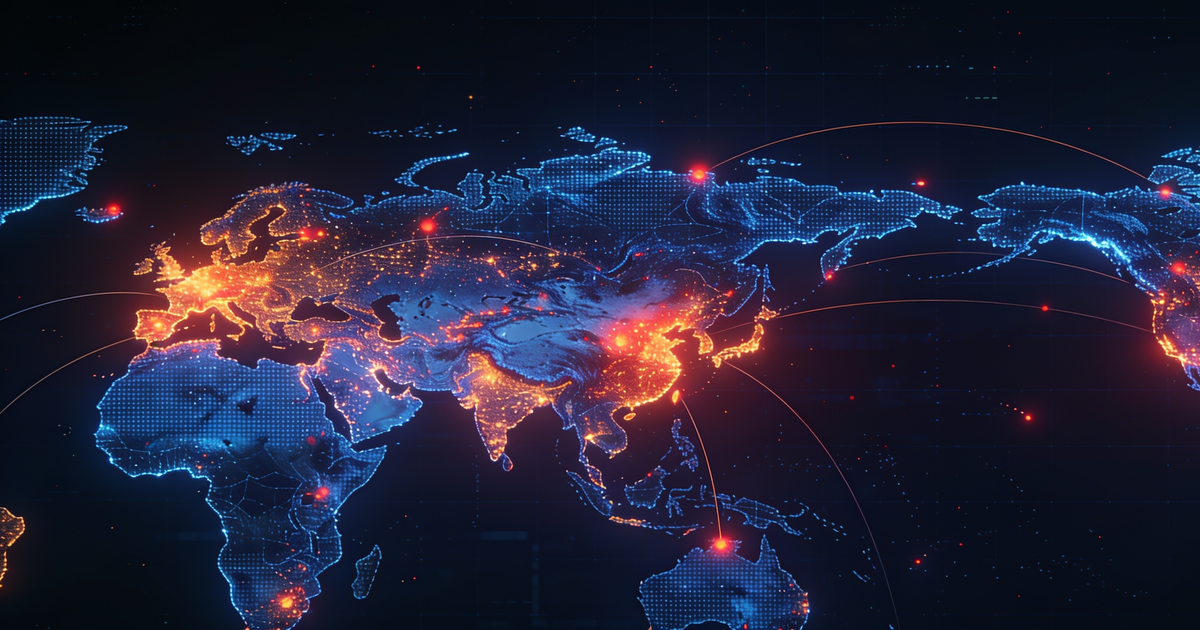
Modern ransomware operations rarely just encrypt files and leave a ransom note. The dominant model since 2020 is double extortion: the gang exfiltrates your data first, then creates a victim entry on their dark-web "leak site" — a public proof-of-breach page with your logo, a sample of stolen documents, and a countdown. Pay, and the entry disappears. Don't, and the data is published or auctioned. Being named on a leak site is public, permanent proof that your organisation was breached — and it is searchable by customers, journalists, regulators, and other criminal groups looking for known-vulnerable targets. Today we're launching a free Ransomware Leak-Site Tracker on 2MNY: a live map of claims worldwide, country and group analytics, and — most importantly — an automatic leak-site check for your domain in every scan we run, including the free tier.
What the Tracker Shows You
The tracker page at 2mny.com/ransomware-tracker is refreshed hourly from community-maintained leak-site monitoring. It answers four questions at a glance:
- Where is ransomware hitting? An interactive world map shades countries by the number of organisations claimed. Click a country to filter every table to that country's victims.
- Who is doing it? A directory of tracked ransomware groups — each with victim counts, suspected locations, and the tools and techniques they favour. The "Most Active Groups" chart ranks groups by tracked claims over the full dataset.
- Who is being hit right now? A live feed of the most recent claims with victim name, sector, group, country, and date — plus a separate cyberattacks feed that flags incidents where infostealer logs (stolen credentials) are also in circulation for the same victim.
- Is my organisation named? Run any 2MNY scan — the free tier included — and the Ransomware Leak-Site Exposure Check looks for your domain across the entire dataset: exact host, parent domain, and subdomains.
The data mirrors what the groups themselves publish on their onion-service leak sites. We aggregate it through community-tracked sources (principally the ransomware.live project) into our own database, refreshed hourly — so the page, and every scan check, runs against a local copy. Scans never touch the dark web.
Why a Leak-Site Listing Matters More Than the Encryption
Teams often assume ransomware is an availability problem: restore from backups, move on. A leak-site listing reframes the incident entirely, because the data is already gone:
- Regulatory clocks start. GDPR Article 33 requires notification to a supervisory authority within 72 hours of becoming aware of a personal-data breach — and exfiltration is a breach even if nothing was encrypted. Sector regulators (healthcare, finance, education) add their own duties.
- Second-wave attacks follow. Once a victim is named, other groups re-target the same organisation — the initial access that worked once is often still open, and freshly-published data reveals internal structure, credentials, and partners.
- Partners and customers are in the data too. Exfiltrated corporate data usually contains third-party information: customer PII, vendor contracts, partner emails. Your breach becomes their incident.
- Negotiation pressure is public. The countdown is designed to make panic a strategy. Having a pre-agreed incident-response plan — including a decision framework for extortion demands — removes the worst decisions from the worst moment.
How the Domain Check Works in a Scan
The Ransomware Leak-Site Exposure Check is now part of the standard scanner suite (it runs in the quick tier, so even free scans include it). Three outcomes are possible:
| Result | Meaning | What we report |
|---|---|---|
| Domain claimed | Your domain matches one or more leak-site victim entries | Critical finding with group name(s), claim date(s), and the claim URL for your incident-response team |
| No claim found | Dataset checked, no match for your domain | Info assurance finding citing the dataset size and freshness — citable in audits and due-diligence responses |
| Dataset unavailable | Local mirror not yet populated (new deployments) | Scanner skips cleanly — we never claim coverage we don't have |
A critical detail on semantics: a leak-site listing means the organisation was breached — not necessarily the website. Ransomware typically enters through the corporate network (phishing, exposed remote access, credential theft, supply chain), while the public site stays technically healthy. That's why we frame the finding as incident-response intelligence rather than a website vulnerability, and why the recommended next steps are organisation-wide: activate IR, assess what was exfiltrated, check notification obligations, hunt the initial-access vector, rotate credentials, and re-scan infrastructure to close technical gaps.
What to Do If Your Domain Appears
If the tracker — or a scan — shows your organisation on a leak site, treat it as a probable active incident even if systems feel fine:
- Activate your incident-response plan and notify the organisation's security leadership immediately. Assume the exfiltration claim is true until proven otherwise.
- Determine what was taken. The claim page usually lists a data sample. Match it against your data inventory: customer records, HR files, financials, source code, contracts.
- Assess legal obligations. GDPR 72-hour notification, sector regulators, contractual breach-notice clauses with customers and partners — loop in counsel early.
- Hunt the initial-access vector across the whole organisation: VPN and remote-access logs, email forensics, endpoint telemetry, exposed services. Patch or contain what you find.
- Rotate credentials comprehensively — especially service accounts, API keys, and any secrets in the exfiltrated data — and review identity systems for persistence.
- Re-scan your external infrastructure with a deep audit and enable continuous monitoring so follow-up changes are caught.
Limitations Worth Knowing
Honesty about what a tracker can and cannot tell you is part of the value. Claims appear when the group decides to publish, which can be days or weeks after the actual intrusion — and quiet payments, abandoned extortion, and never-published thefts never appear at all. "No listing" is therefore an assurance signal, not proof of no breach. Pair it with technical scanning: exposed panels, leaked secrets and API keys, SSL weaknesses, and misconfigurations are the precursors ransomware groups actually exploit, and those are exactly what a 2MNY deep scan is built to surface. Continuous-monitoring customers get the leak-site check re-run automatically every hour, so a new claim against their domain pages the security team rather than waiting for the next quarterly audit.
Check Your Domain Now
The tracker is free to browse, no account needed: 2mny.com/ransomware-tracker. To check your own domain against the full dataset — plus 234 security tests including secret-leak and API-key exposure checks — run a free security scan. If you'd rather have the hourly automatic version with alerting, continuous monitoring covers it.